Solutions · CIO
Connect cyber governance to technology strategy.
Bring cyber posture into IT portfolio decisions, M&A diligence and vendor risk with one governance graph.
Why this role struggles
Today's reality without governance intelligence.
- Cyber and IT operate in parallel governance worlds.
- Technology risk is reported, not governed.
- Vendor and M&A risk is rebuilt from scratch every time.
Why existing tools fail
GRC, GRC-lite and homegrown trackers.
- ITSM tools track changes, not governance decisions.
- Vendor risk tools generate forms, not posture.
- BI dashboards cannot show accountability.
How XRegula helps
Continuous governance loop, decision-first.
- Single graph for cyber, IT and vendor governance.
- Decision rights aligned with technology investment.
- Reusable evidence across vendor, audit and M&A workflows.
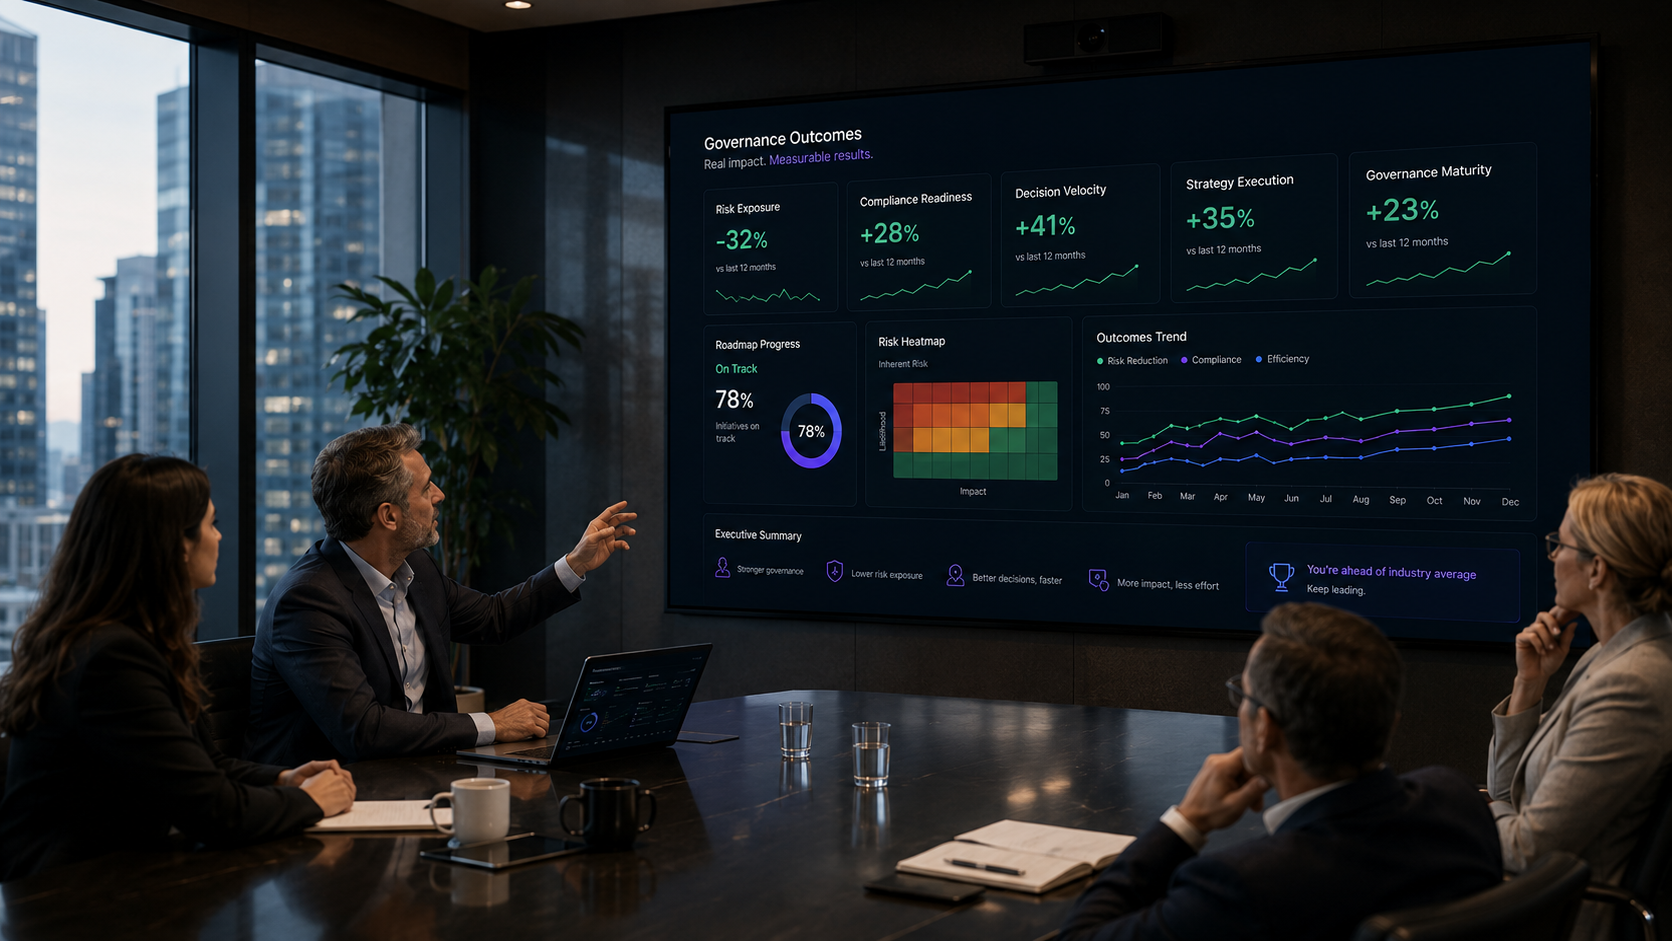
Expected outcomes
Tangible governance lift.
1
graph for cyber + IT
+40%
vendor governance speed
−50%
duplicated evidence
+1 score
per quarter